Artificial intelligence is like hiring the fastest summer student in Canadian history.
It can summarize a document in seconds. Draft an email before you finish your coffee. Organize notes, explain formulas and suggest ten ways to improve a process.
Very impressive.
It can also make mistakes and receive information it should never have been given.
That is why AI should not wander freely through an accounting firm without rules.
The question is no longer whether employees are curious about these tools.
They are.
The real question is whether your firm has explained what is safe.
The Helpful Shortcut That Creates the Problem
Picture a junior accountant receiving a long client email.
It contains details about an estate, payroll issue or business transaction. To save time, they paste it into a public AI tool and ask for a summary.
Five minutes saved.
Potential privacy problem created.
The message may contain a client name, financial figures, banking details or tax information.
That information was entrusted to your professionals for a specific purpose.
It was not donated to the internet’s largest suggestion box.
Employees usually do this because the tool is convenient and nobody has explained the boundary.
Without a policy, every staff member invents their own rules.
That is not innovation.
That is improvisation with client data.
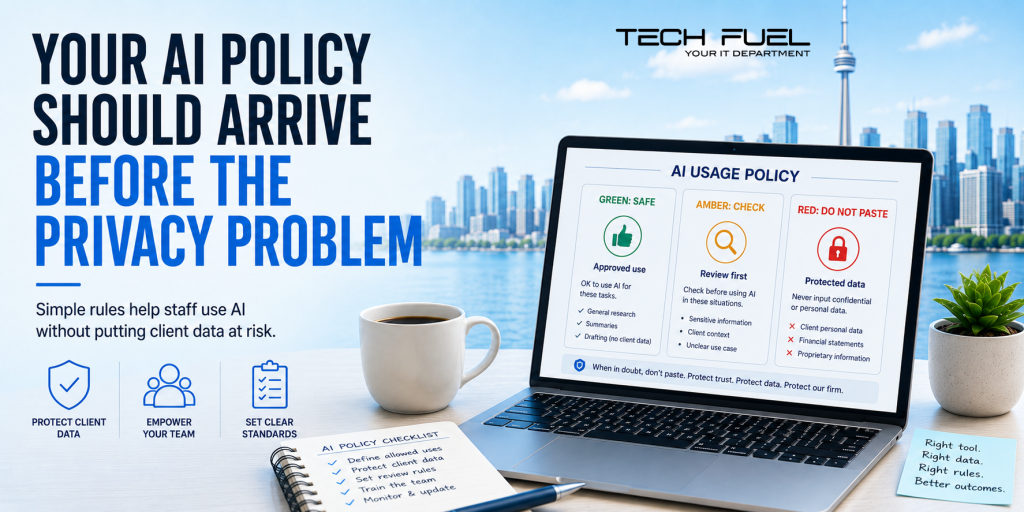
Use a Simple Traffic-Light Rule
Your first AI policy does not need to be forty pages long.
Start with something employees can remember.
Green: Generally Safe
Green activities use public or non-confidential information.
Examples include drafting a generic meeting agenda, rewording public marketing copy, explaining an Excel formula or brainstorming for an internal meeting.
No client information goes into the prompt.
Amber: Stop and Check
Amber activities may be useful, but require approval.
This could include using a firm-approved business AI platform, summarizing material after client identifiers have been removed or uploading documents through an approved workflow.
Amber does not mean “never.”
It means “do not make this decision alone.”
Red: Do Not Paste
Red information should never be entered into an unapproved public AI tool.
That includes tax returns, T4 or T5 information, social insurance numbers, banking details, payroll records and client financial statements.
If the information would cause a partner to leap across the boardroom table and grab the keyboard, it belongs in the red zone.
The Five-Line AI Policy
Your firm can begin with five rules:
- Use only tools approved by the firm.
- Do not enter identifiable client information.
- Check every answer before relying on it.
- A qualified person remains responsible for the final work.
- Report accidental disclosure immediately.
Those five lines give employees a practical starting point.
They also make one thing clear: a polished AI answer is not automatically a correct one.
AI Should Be a Junior Assistant
AI can summarize, organize, draft and suggest.
But it should not receive signing authority, independent access to client files or permission to make professional judgments while everyone else is at lunch.
Treat it like a talented new employee.
Give it boundaries. Check its work. Never hand it the vault combination.
Ask your IT provider whether the firm can identify and control which AI applications employees use with company accounts and data.
A policy nobody can support or monitor is really just a polite suggestion.
Schedule a 10-minute discovery call with us to review how AI is being used inside your firm and create practical safeguards around client information.
Because AI can be a brilliant assistant.
It should never become an unsupervised one.
Call us at 1-855-737-8277, book a quick Discovery Call, or view our I.T. Buyers Guide.